Asos confirms customer data 'may have been accessed' after hackers turn its own app into a ransom note
From the Newshound archive · first published 6 October 2026 · last updated 7 October 2026.
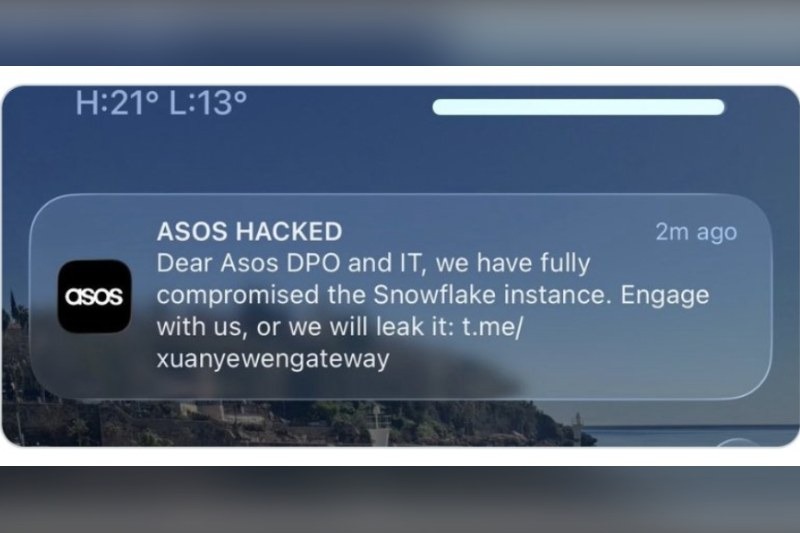
Hackers infiltrated Asos's Snowflake data platform and turned the fashion retailer's own mobile app into an extortion tool, bombarding millions of customers with a threatening message ordering bosses to "engage or we will leak it." Asos confirmed that customer names and contact details may have been accessed, though it emphasised that payment card information and passwords were not compromised. GCHQ's National Cyber Security Centre has stepped in to offer assistance while the investigation is ongoing.
The group responsible, which calls itself Xuanye, weaponised Asos's own push-notification system to deliver its ransom demand — a tactic cybersecurity experts described as "unusually brazen."
Analysts at AJ Bell cautioned that the attack came "at a terrible time," hitting the retailer just as its turnaround plan was beginning to bear fruit after prolonged losses.
Security experts are urging Asos's 16.5 million customers to stay alert to phishing scams capitalising on the incident, advising them to avoid clicking any links connected to the breach.